Private security and intelligence
Intelligence Central.
Intelligence, analysis and protection for organizations that cannot afford to be wrong.
What we do
Intelligence and protection, under one roof.
Our platform, analysts and field teams work as one continuous operation, from the boardroom brief to the ground.
Threat monitoring
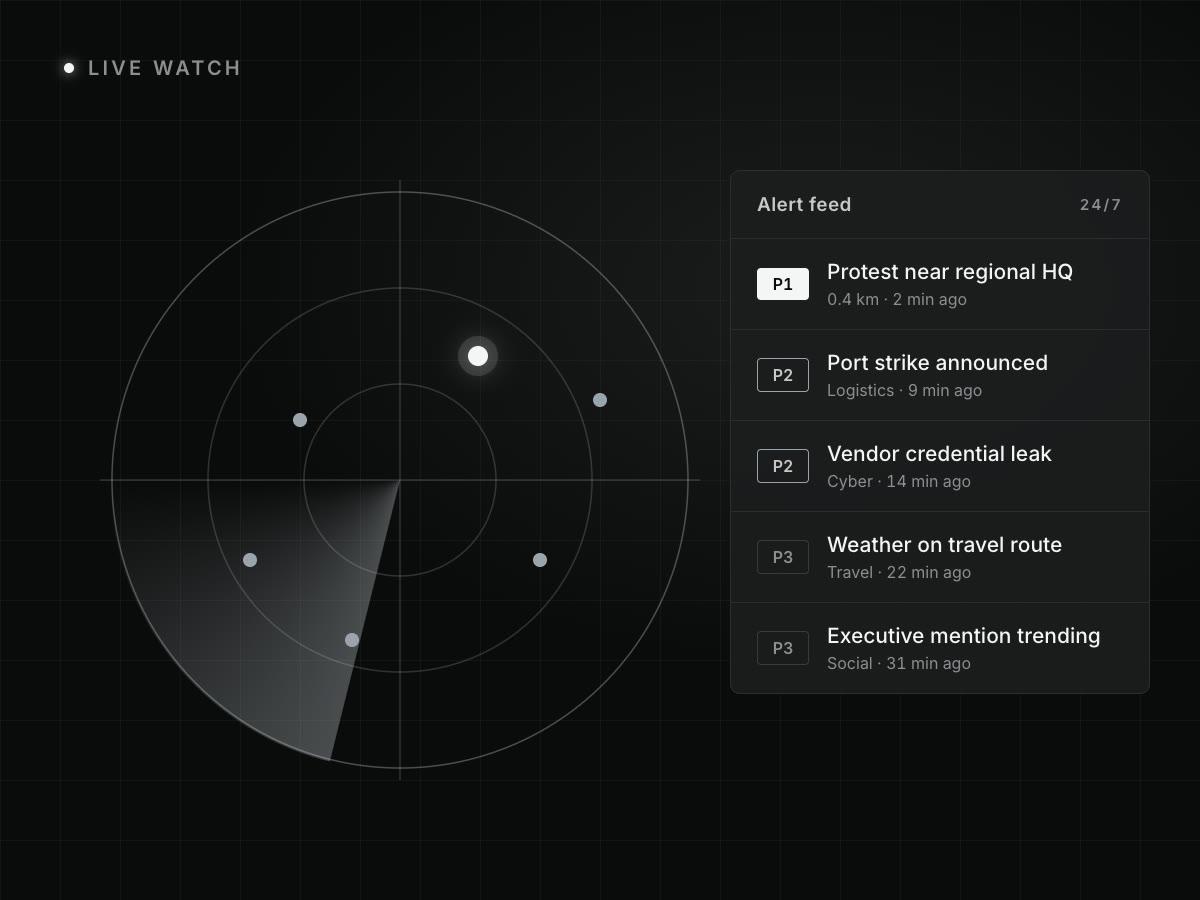
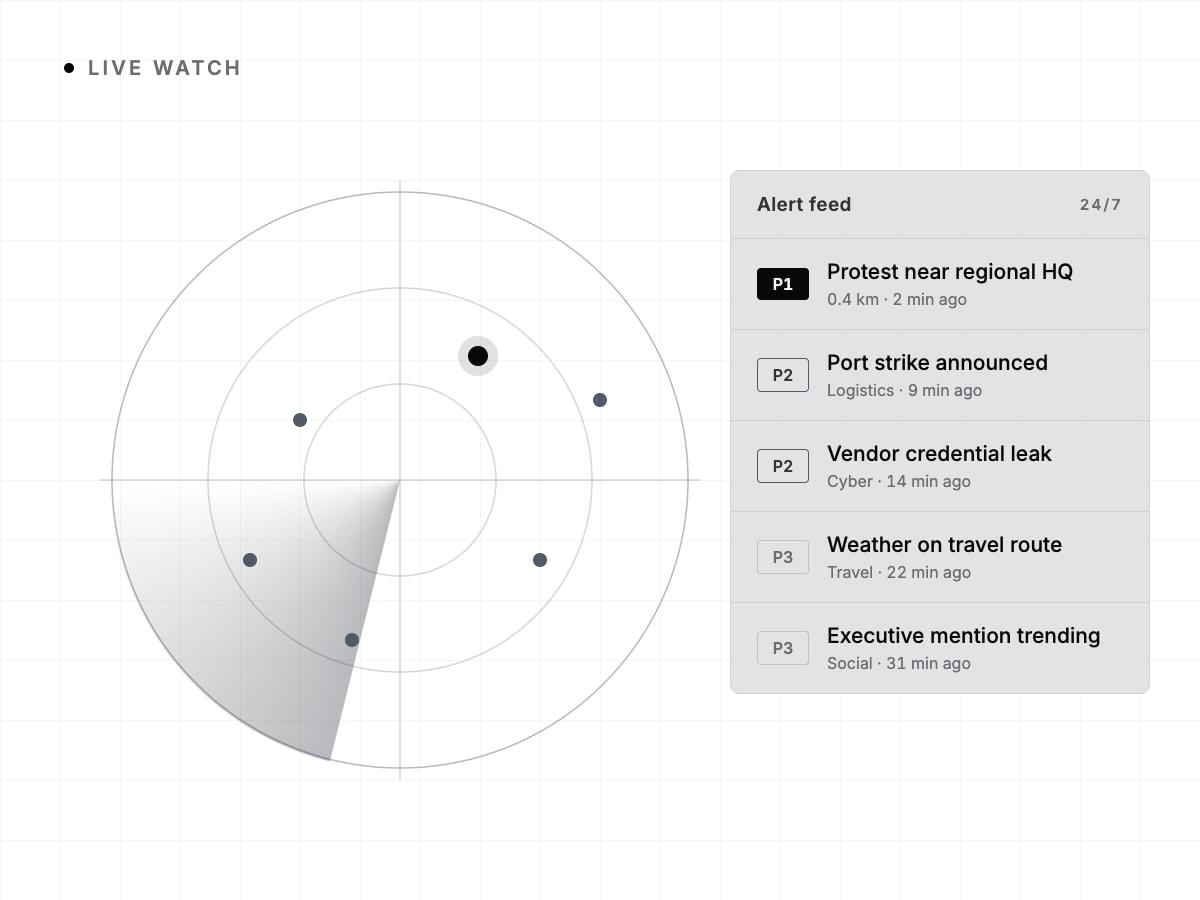
Around-the-clock intelligence tuned to your people, sites, sector and supply chain, not generic advisories.
Learn more →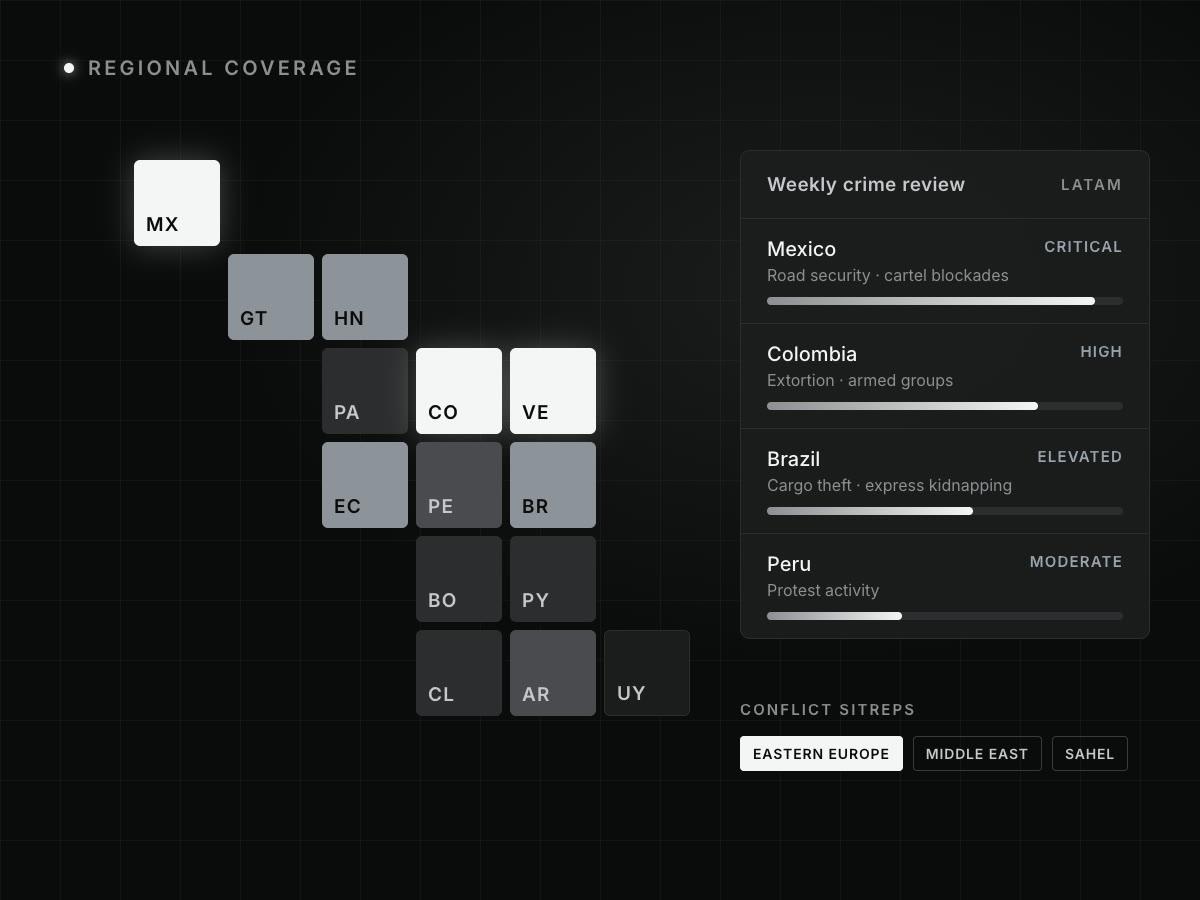
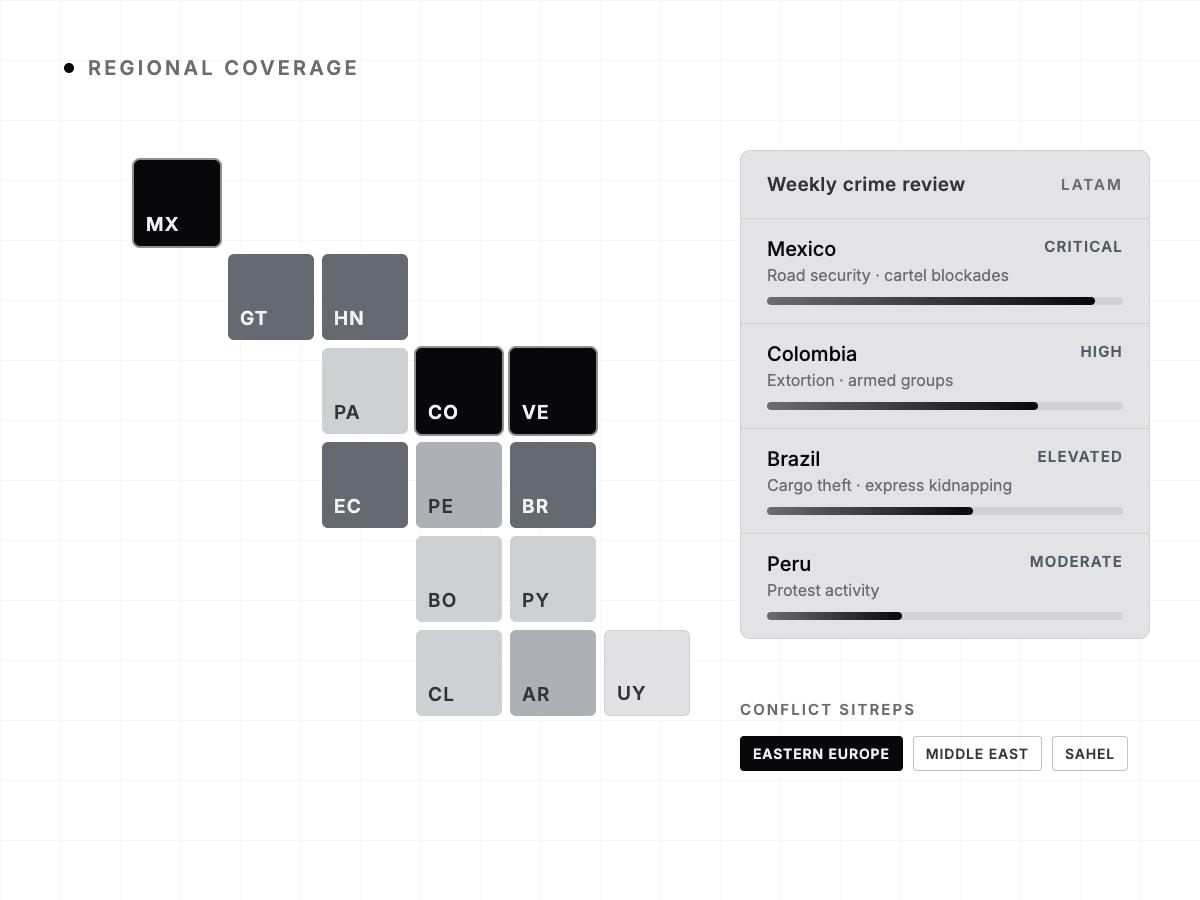
Regional coverage
Country and regional intelligence, with deep coverage of Latin American crime and conflict zones worldwide.
Learn more →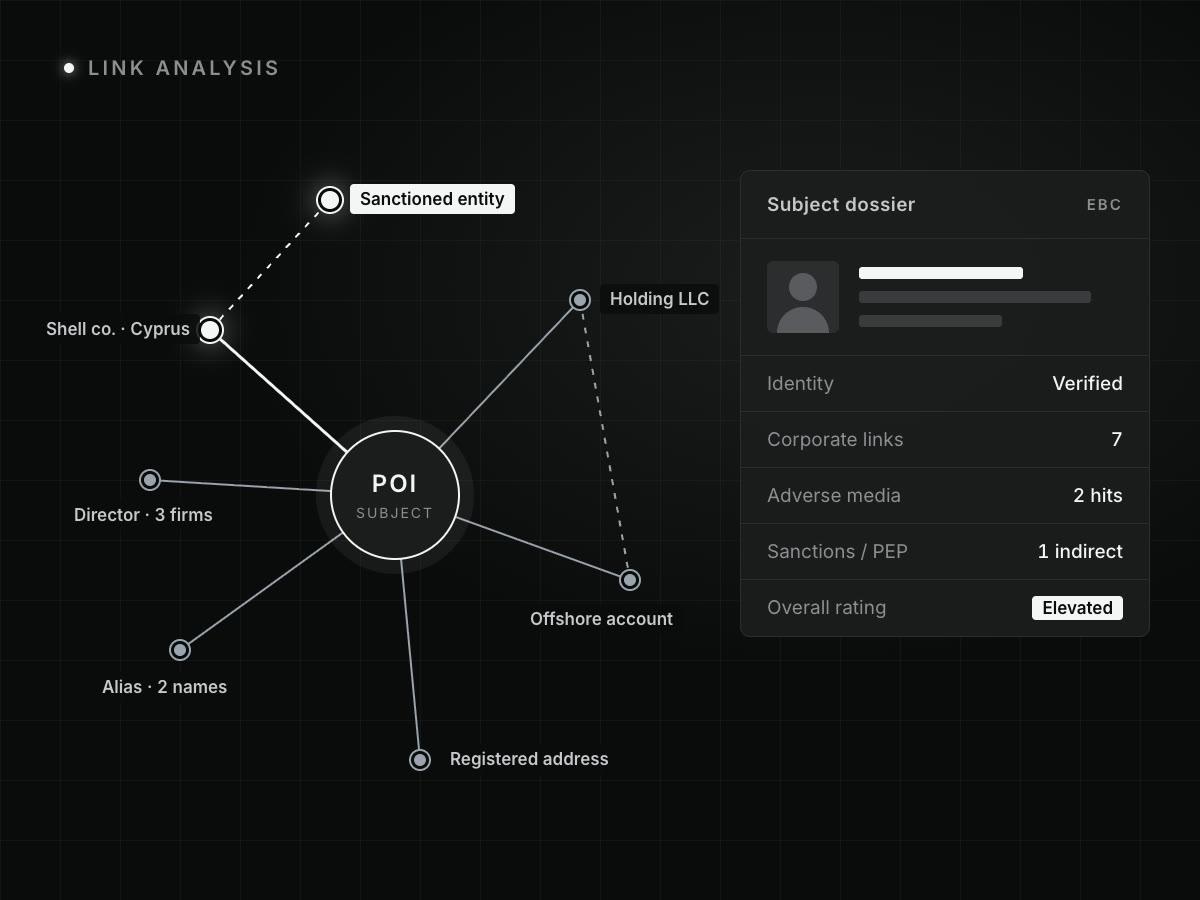
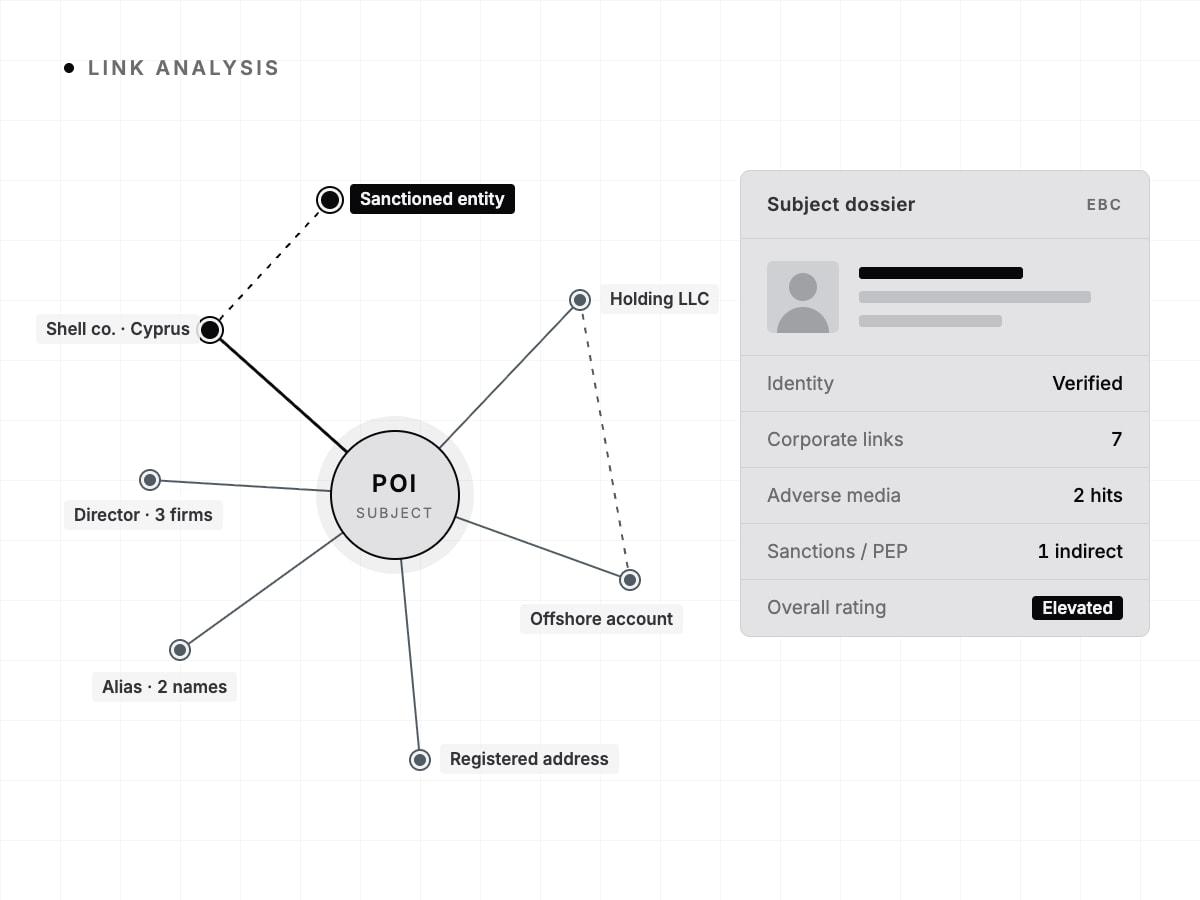
Investigations
Background checks, due diligence and insider-threat investigations that map the people and entities behind a risk.
Learn more →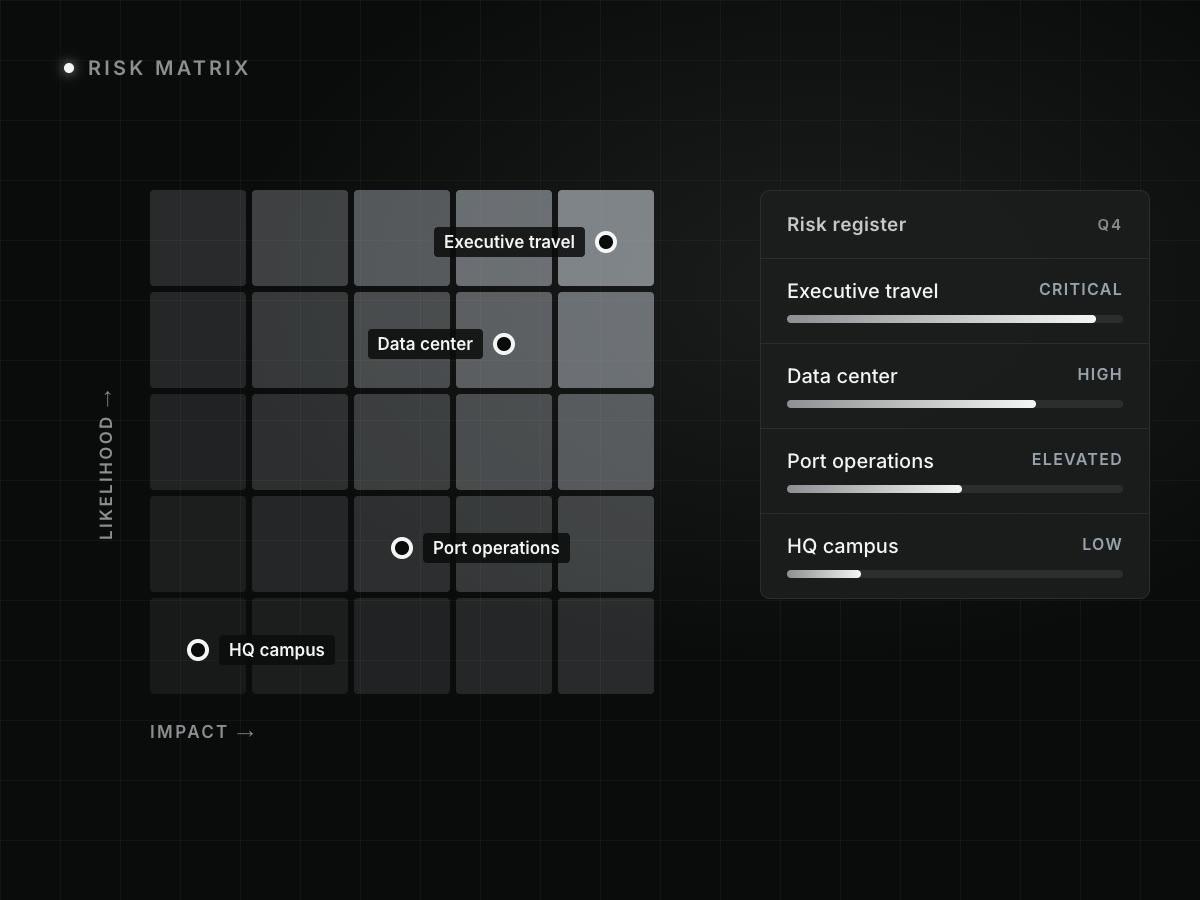
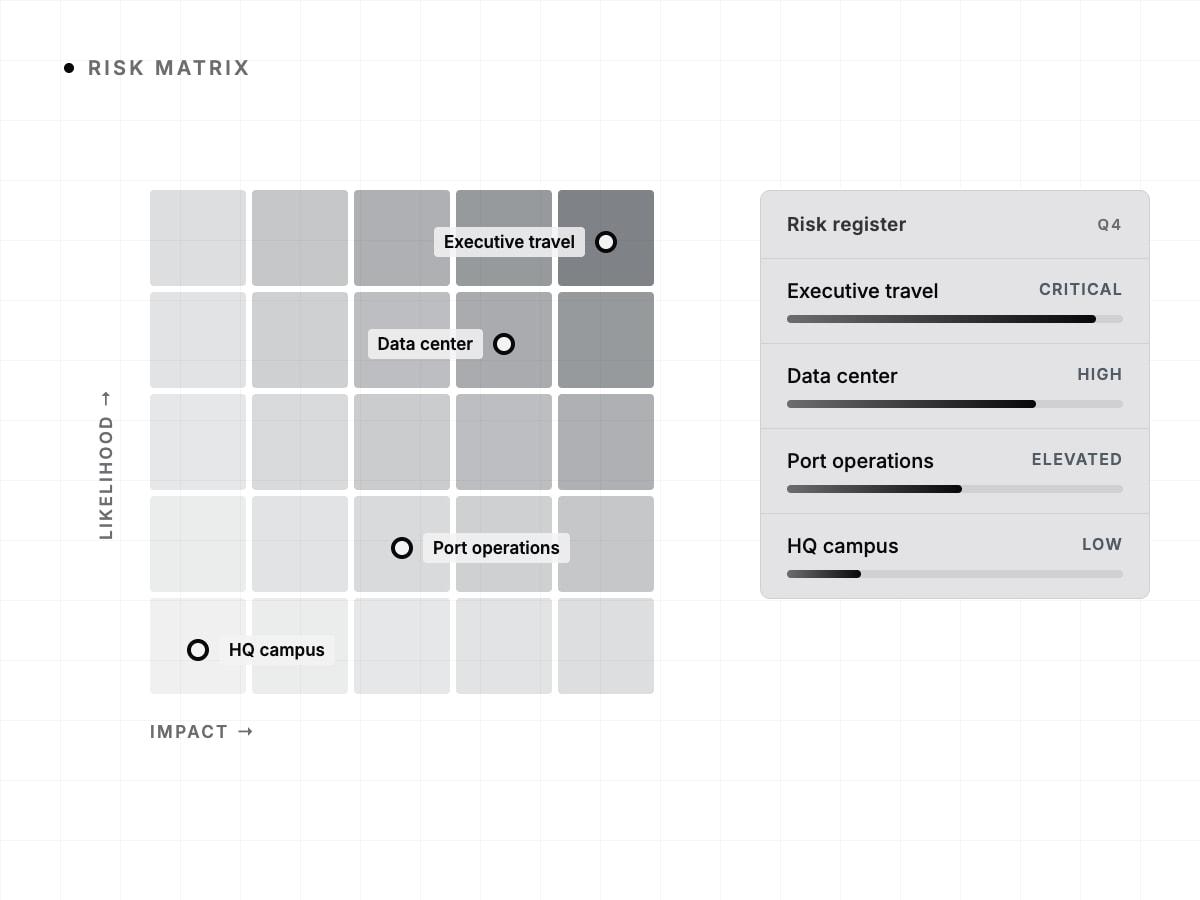
Risk assessment
A proven method that scores risk to people, data, systems and physical assets, so leaders can decide with confidence.
Learn more →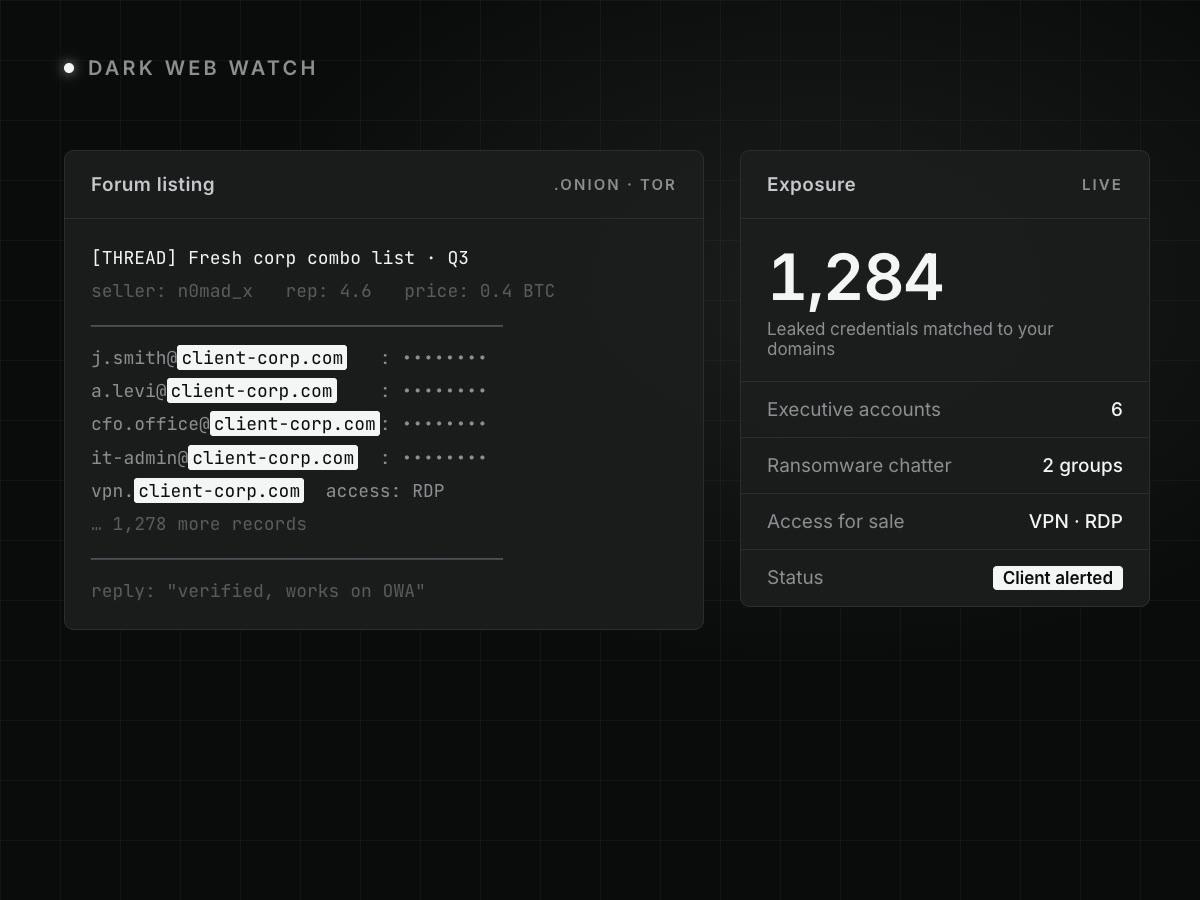
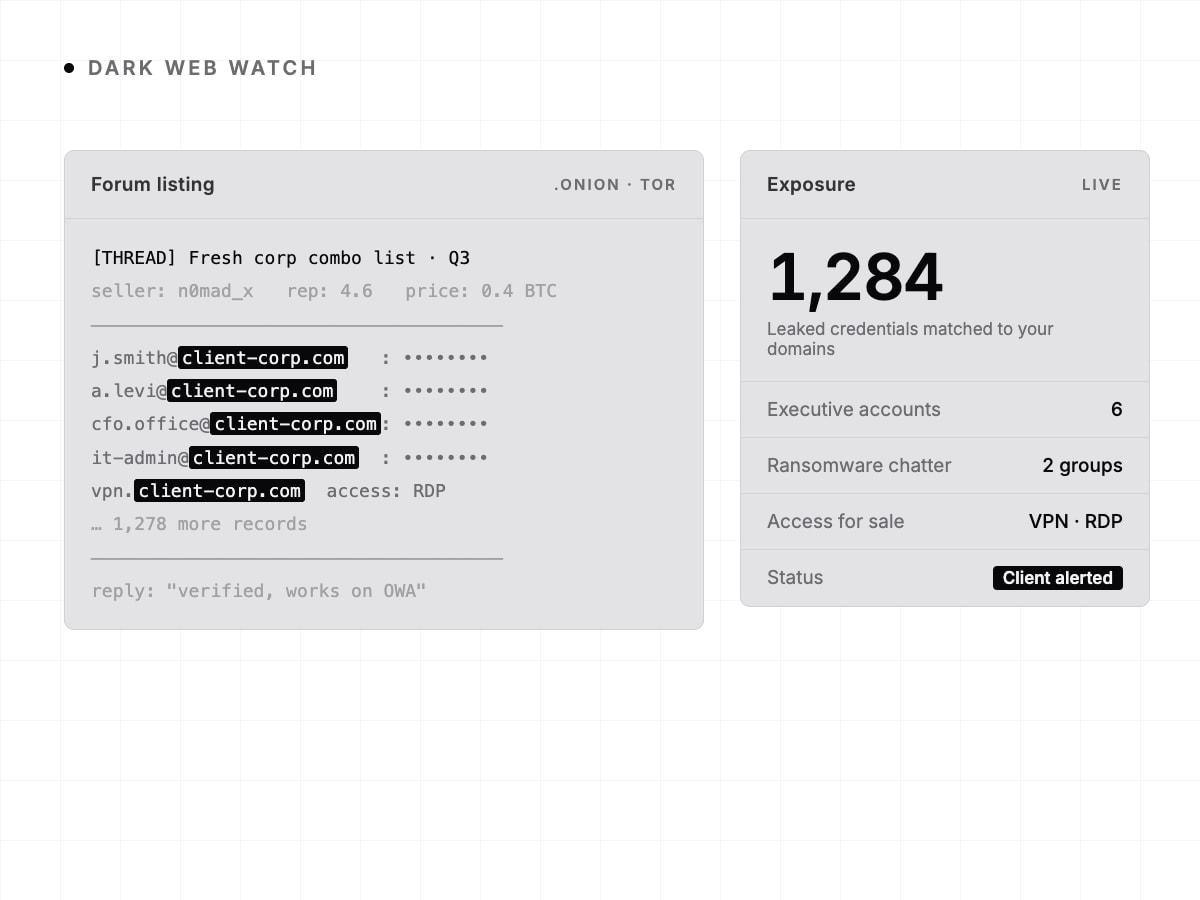
Cyber intelligence
Dark web monitoring that finds leaked credentials, access for sale and ransomware chatter before they are used.
Learn more →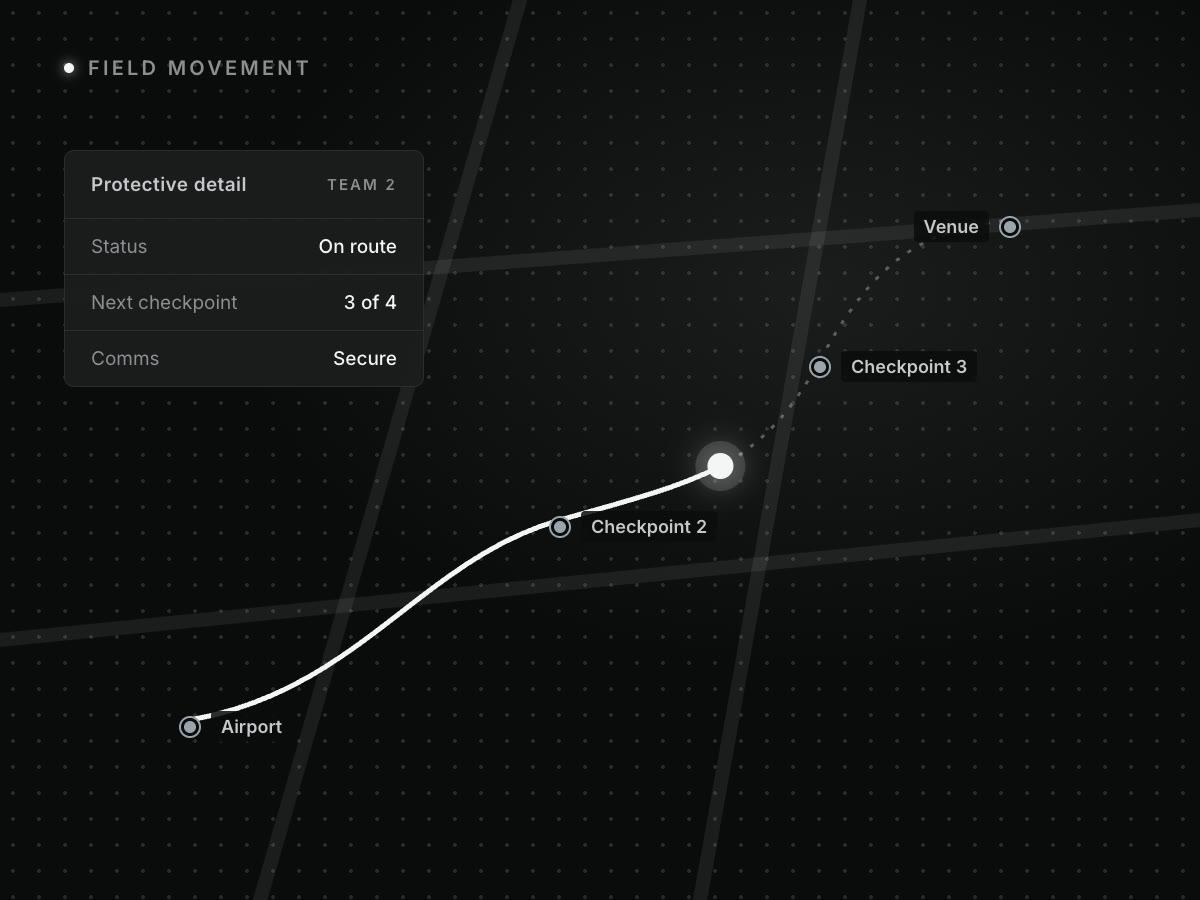
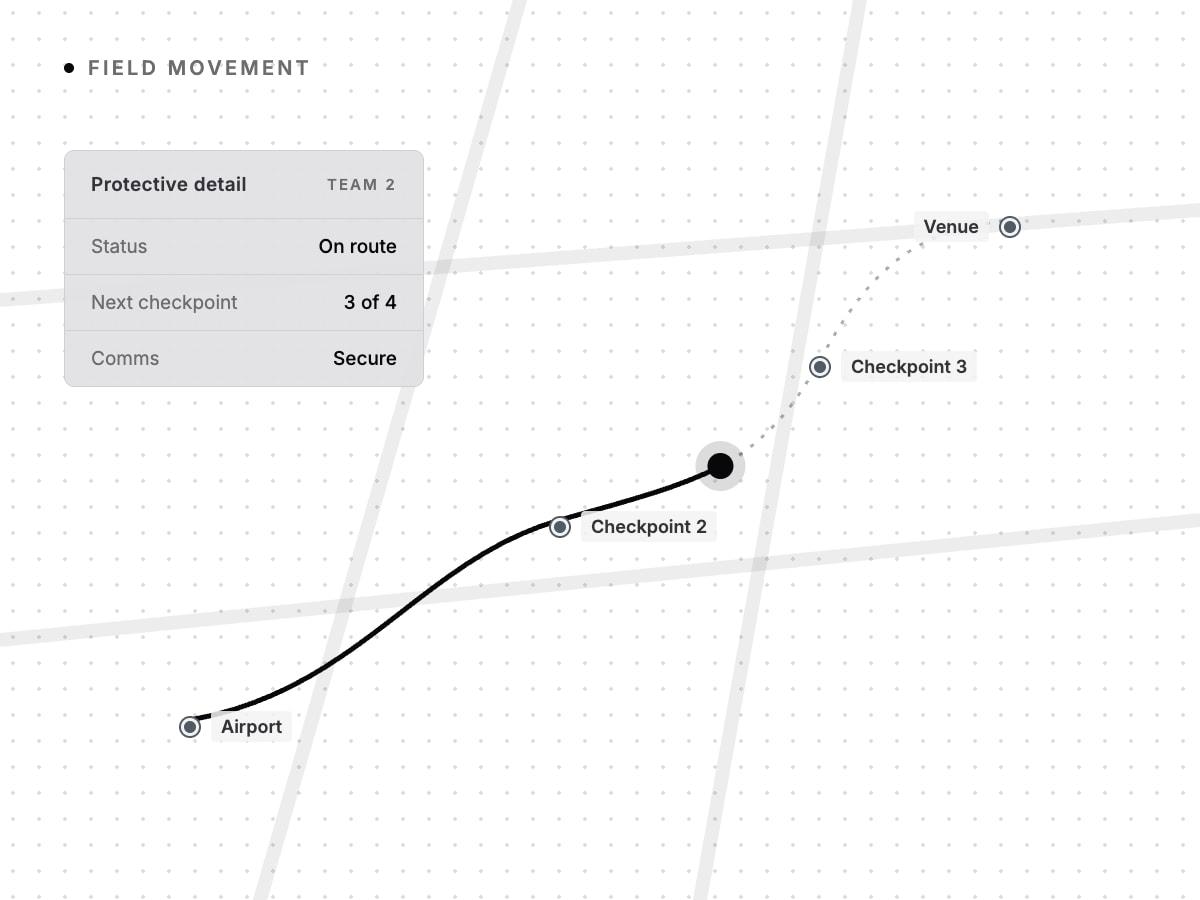
Global field operations
Executive protection, extraction, kidnap and ransom response, and analysts embedded in your security team.
Learn more →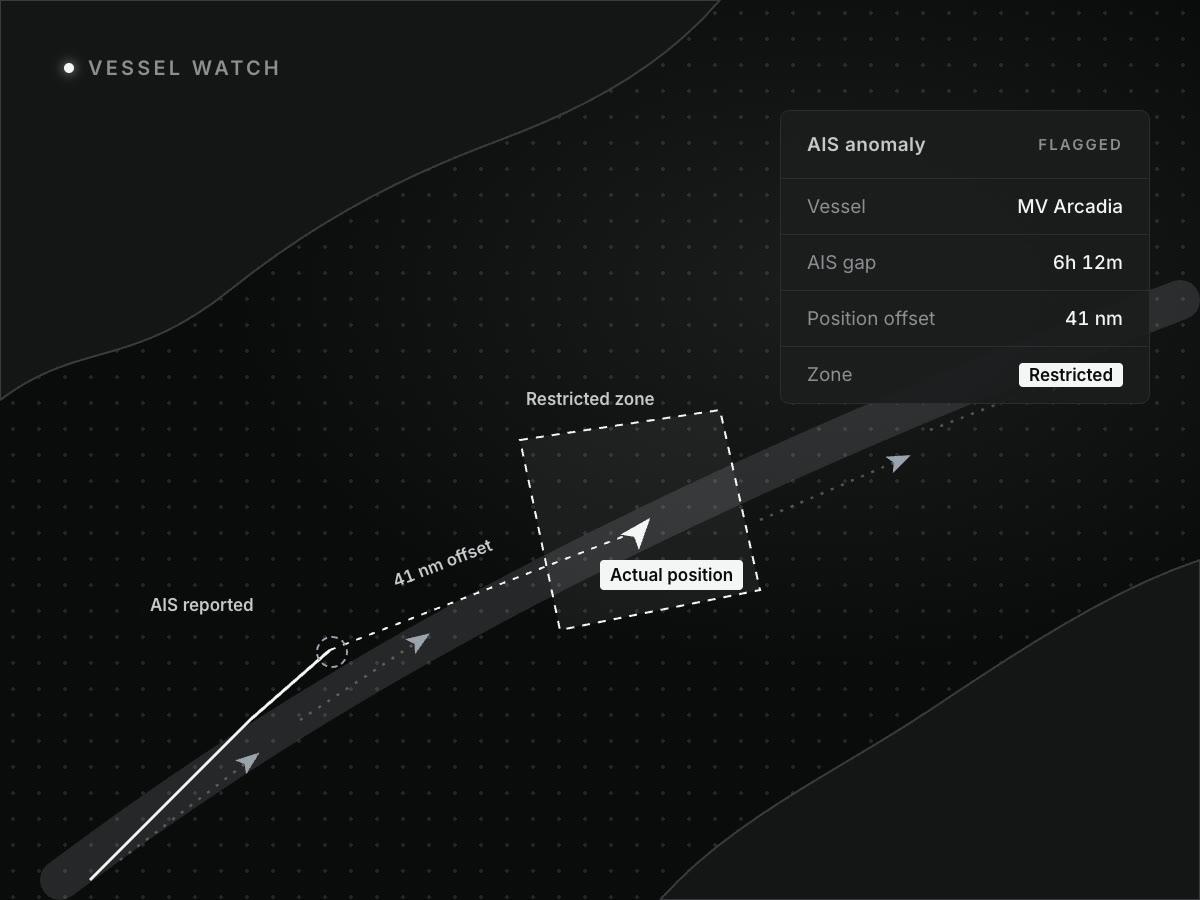
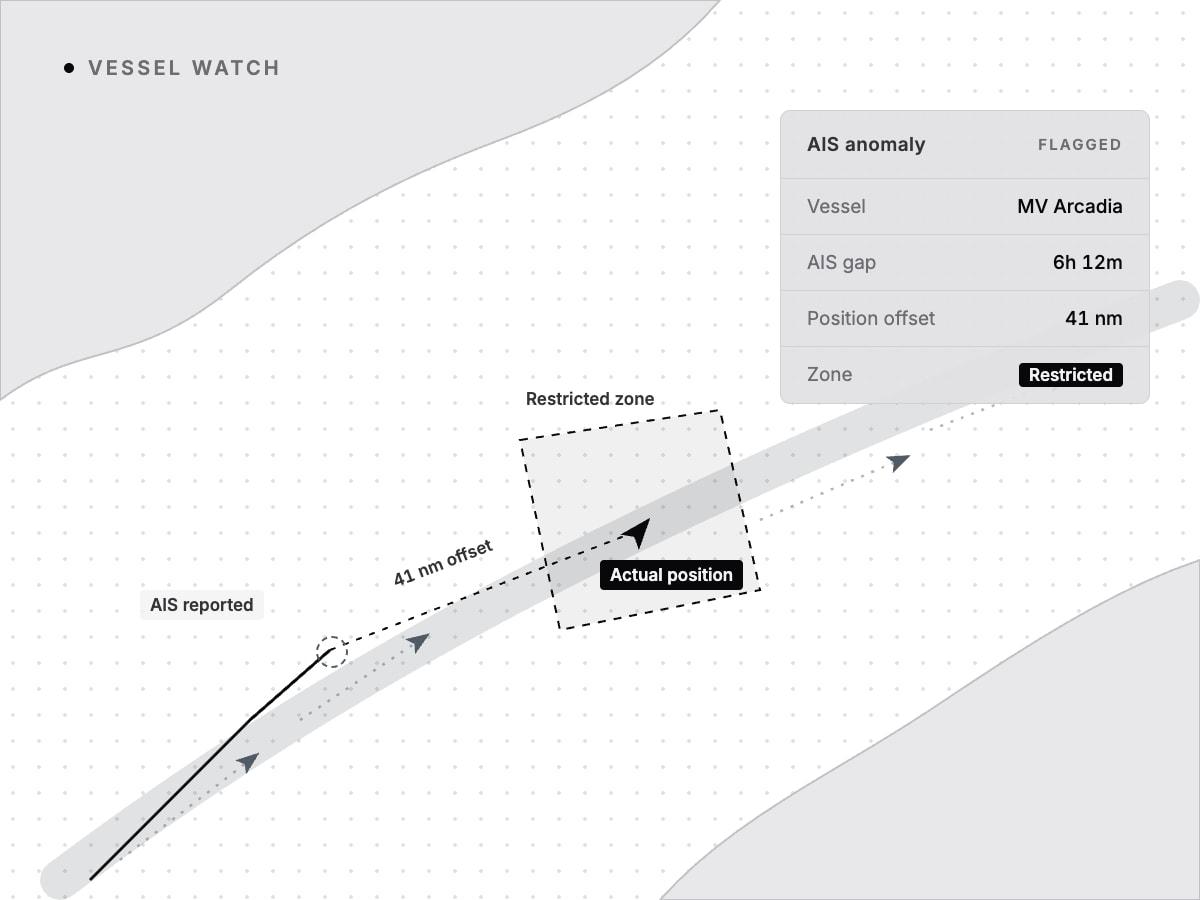
Maritime intelligence
AIS-driven vessel monitoring that flags spoofing, dark activity and zone violations around your fleet and routes.
Learn more →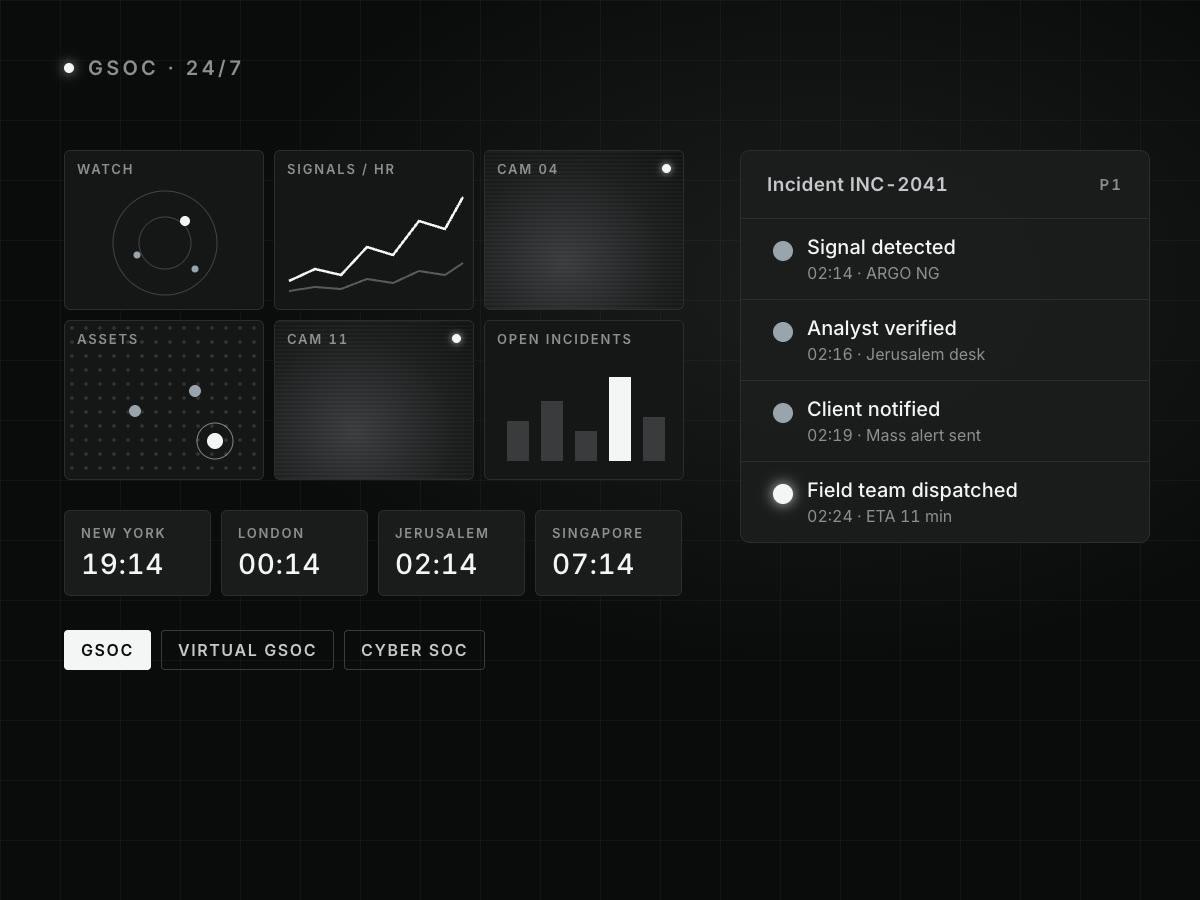
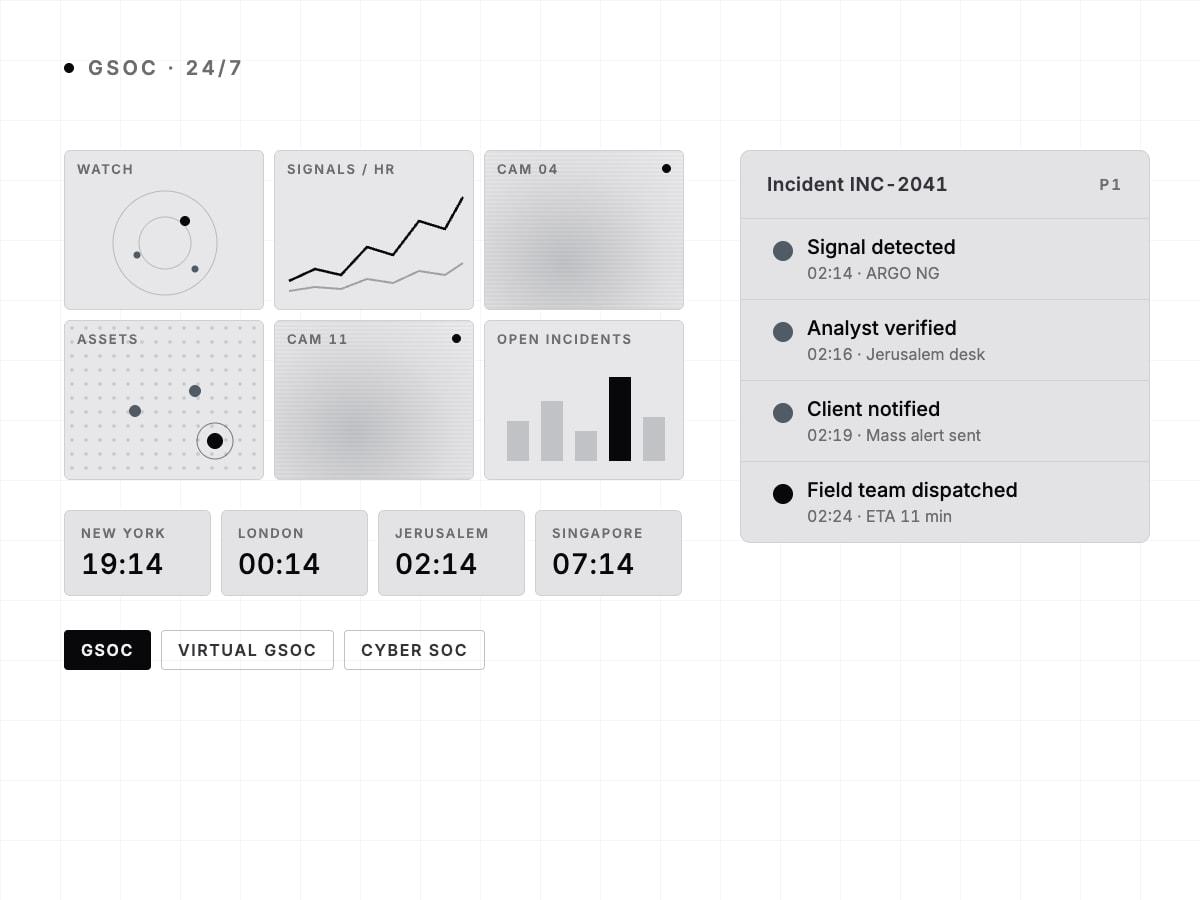
Operations centers
Global and virtual security operations centers that detect, verify and escalate incidents 24/7.
Learn more →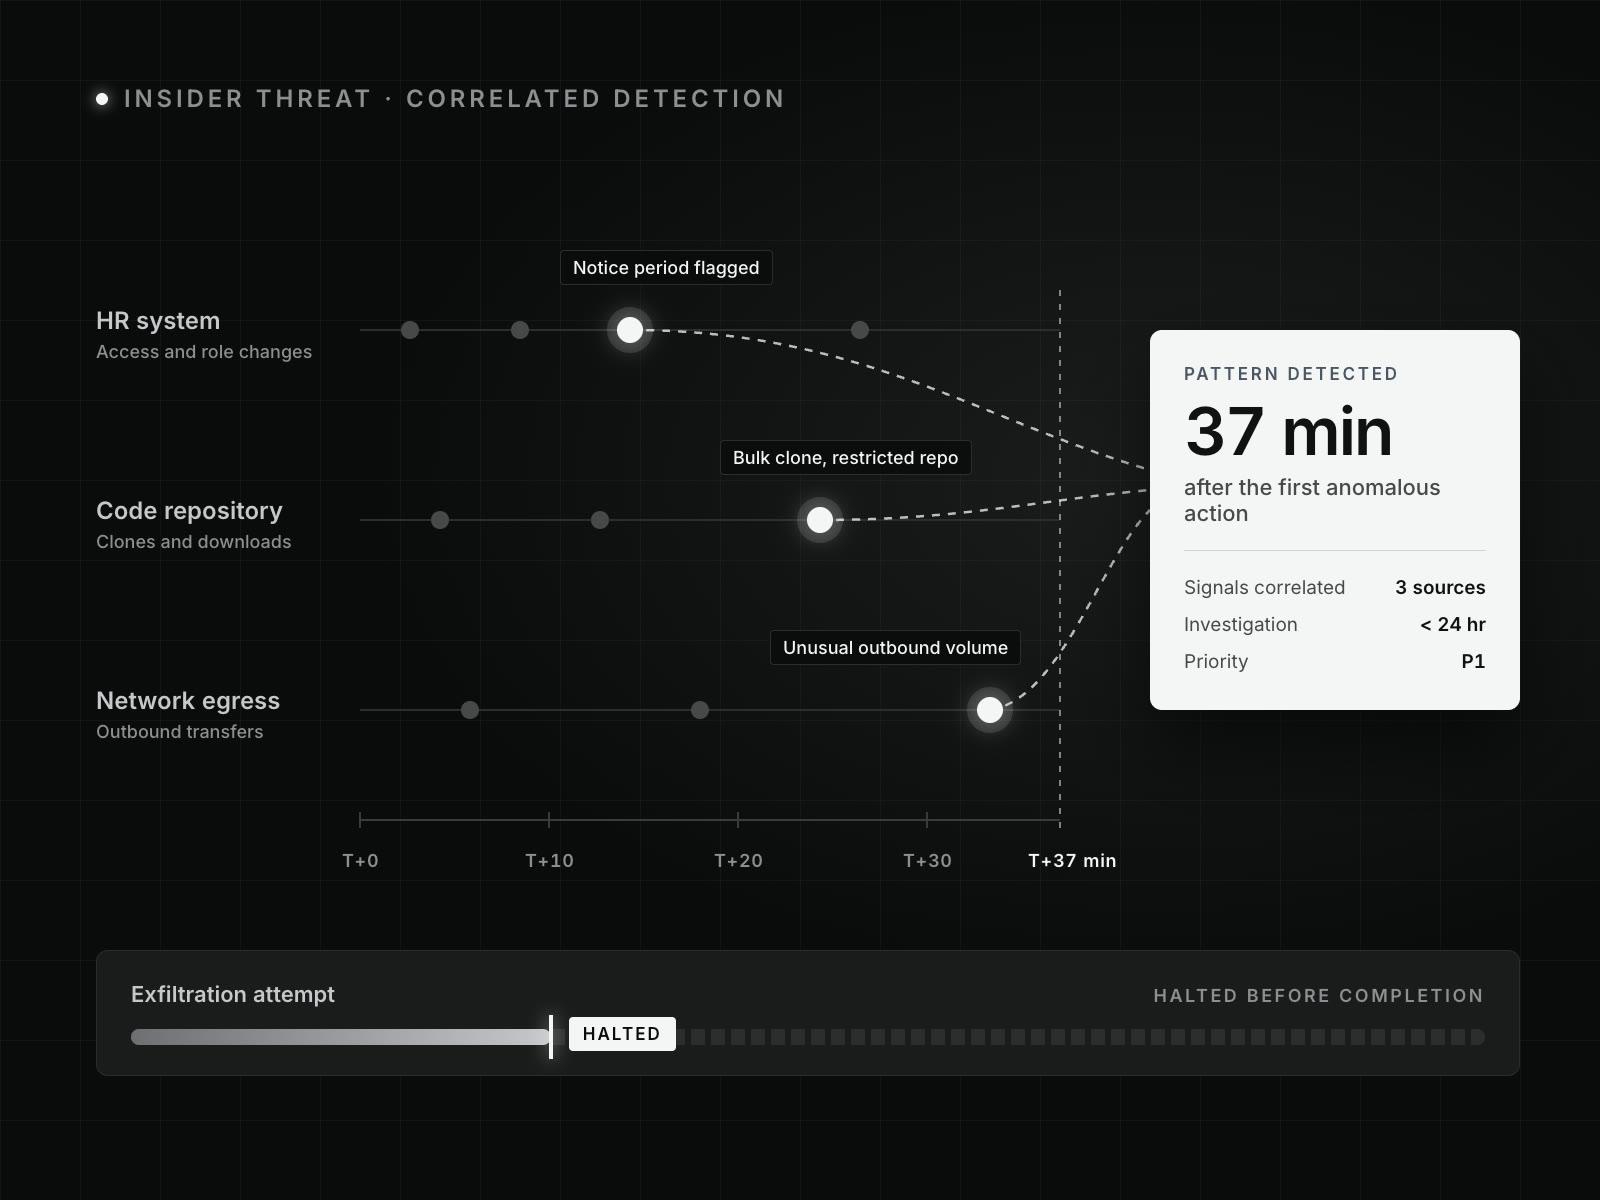
Case study · Defense · United States
Insider IP theft, stopped before it was complete.
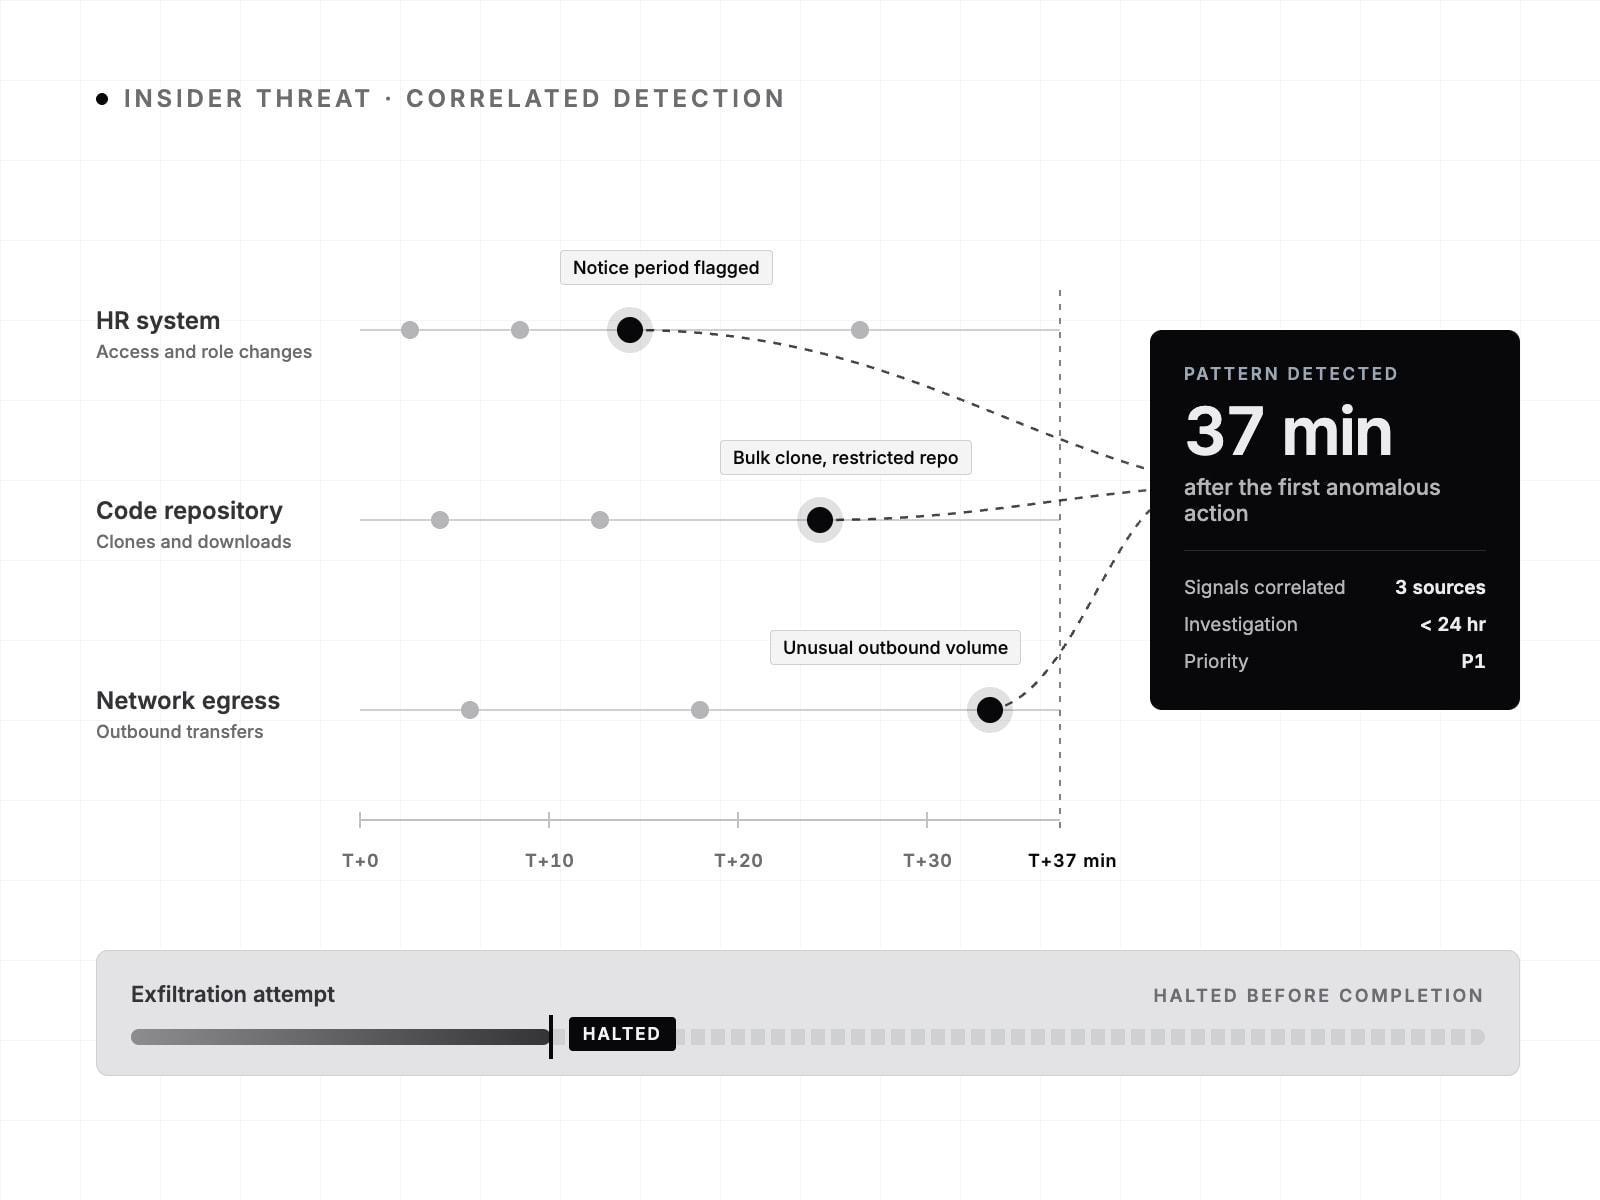
A defense-sector client suspected an internal actor was exfiltrating sensitive IP. They had no risk matrix, no correlation across HR, repository, and network data, and roughly 30 days before contractual disclosure obligations came due.
Pattern detection landed 37 minutes after the first anomalous action. The internal investigation was triggered within 24 hours. All identified IP was recovered before exfiltration completed, and the actor was prosecuted.
- 37 min
- Pattern detection lag
- 100%
- Identified IP recovered
- < 24 hr
- Internal response time
Our platform
ARGO NG
The platform behind Intelligence Central. ARGO NG brings human, technical, open-source and geospatial inputs into one command environment, so analysts see one picture and leaders get one answer.
- Multi-source collection and fusion at scale
- Structured scoring for threat, urgency and proximity
- Escalation and executive-ready reporting, with an analyst on every decision
Global reach
Coverage that follows the threat.
Monitoring zones and fusion centers across five regions, with field reach in 56 countries.
- Philadelphia
- Manama
- Jerusalem
- Singapore
- Riyadh
- Washington (DCA-01) - P1 hotspot at 38.90°, -77.00°
- Tel Aviv (TLV-02) - P1 hotspot at 32.08°, 34.78°
- Kyiv (KBP-03) - P1 hotspot at 50.45°, 30.52°
- Dubai (DXB-04) - P1 hotspot at 25.20°, 55.27°
- Beirut (BEY-05) - P1 hotspot at 33.89°, 35.50°
- London (LHR-06) - P3 hotspot at 51.50°, -0.12°
- Mexico City (MEX-07) - P2 hotspot at 19.43°, -99.13°
- Bogotá (BOG-08) - P2 hotspot at 4.71°, -74.07°
- Nairobi (NBO-09) - P2 hotspot at -1.29°, 36.82°
- Lagos (LOS-10) - P2 hotspot at 6.52°, 3.38°
- Taipei (TPE-11) - P2 hotspot at 25.03°, 121.56°
- Singapore (SIN-12) - P2 hotspot at 1.35°, 103.82°
Client voices
Trusted when it matters most.
“TAM-C is an extension of our intelligence department. We rely on them for real-time, actionable intelligence, and they have proven themselves over and over again.”
“TAM-C stayed by our side throughout the pandemic when we nearly lost our business, providing priority alerts and weekly intelligence periodicals.”
“TAM-C provided our protection teams with real-time intelligence that guided the team and the principal away from harm. We rely on them during planning and movement.”
When you need to know, before everyone else does.
Initial conversations are confidential. Most engagements begin with a rapid threat assessment.